Ongoing Security-Flaw Scanning & Patch Tracking
What You Get
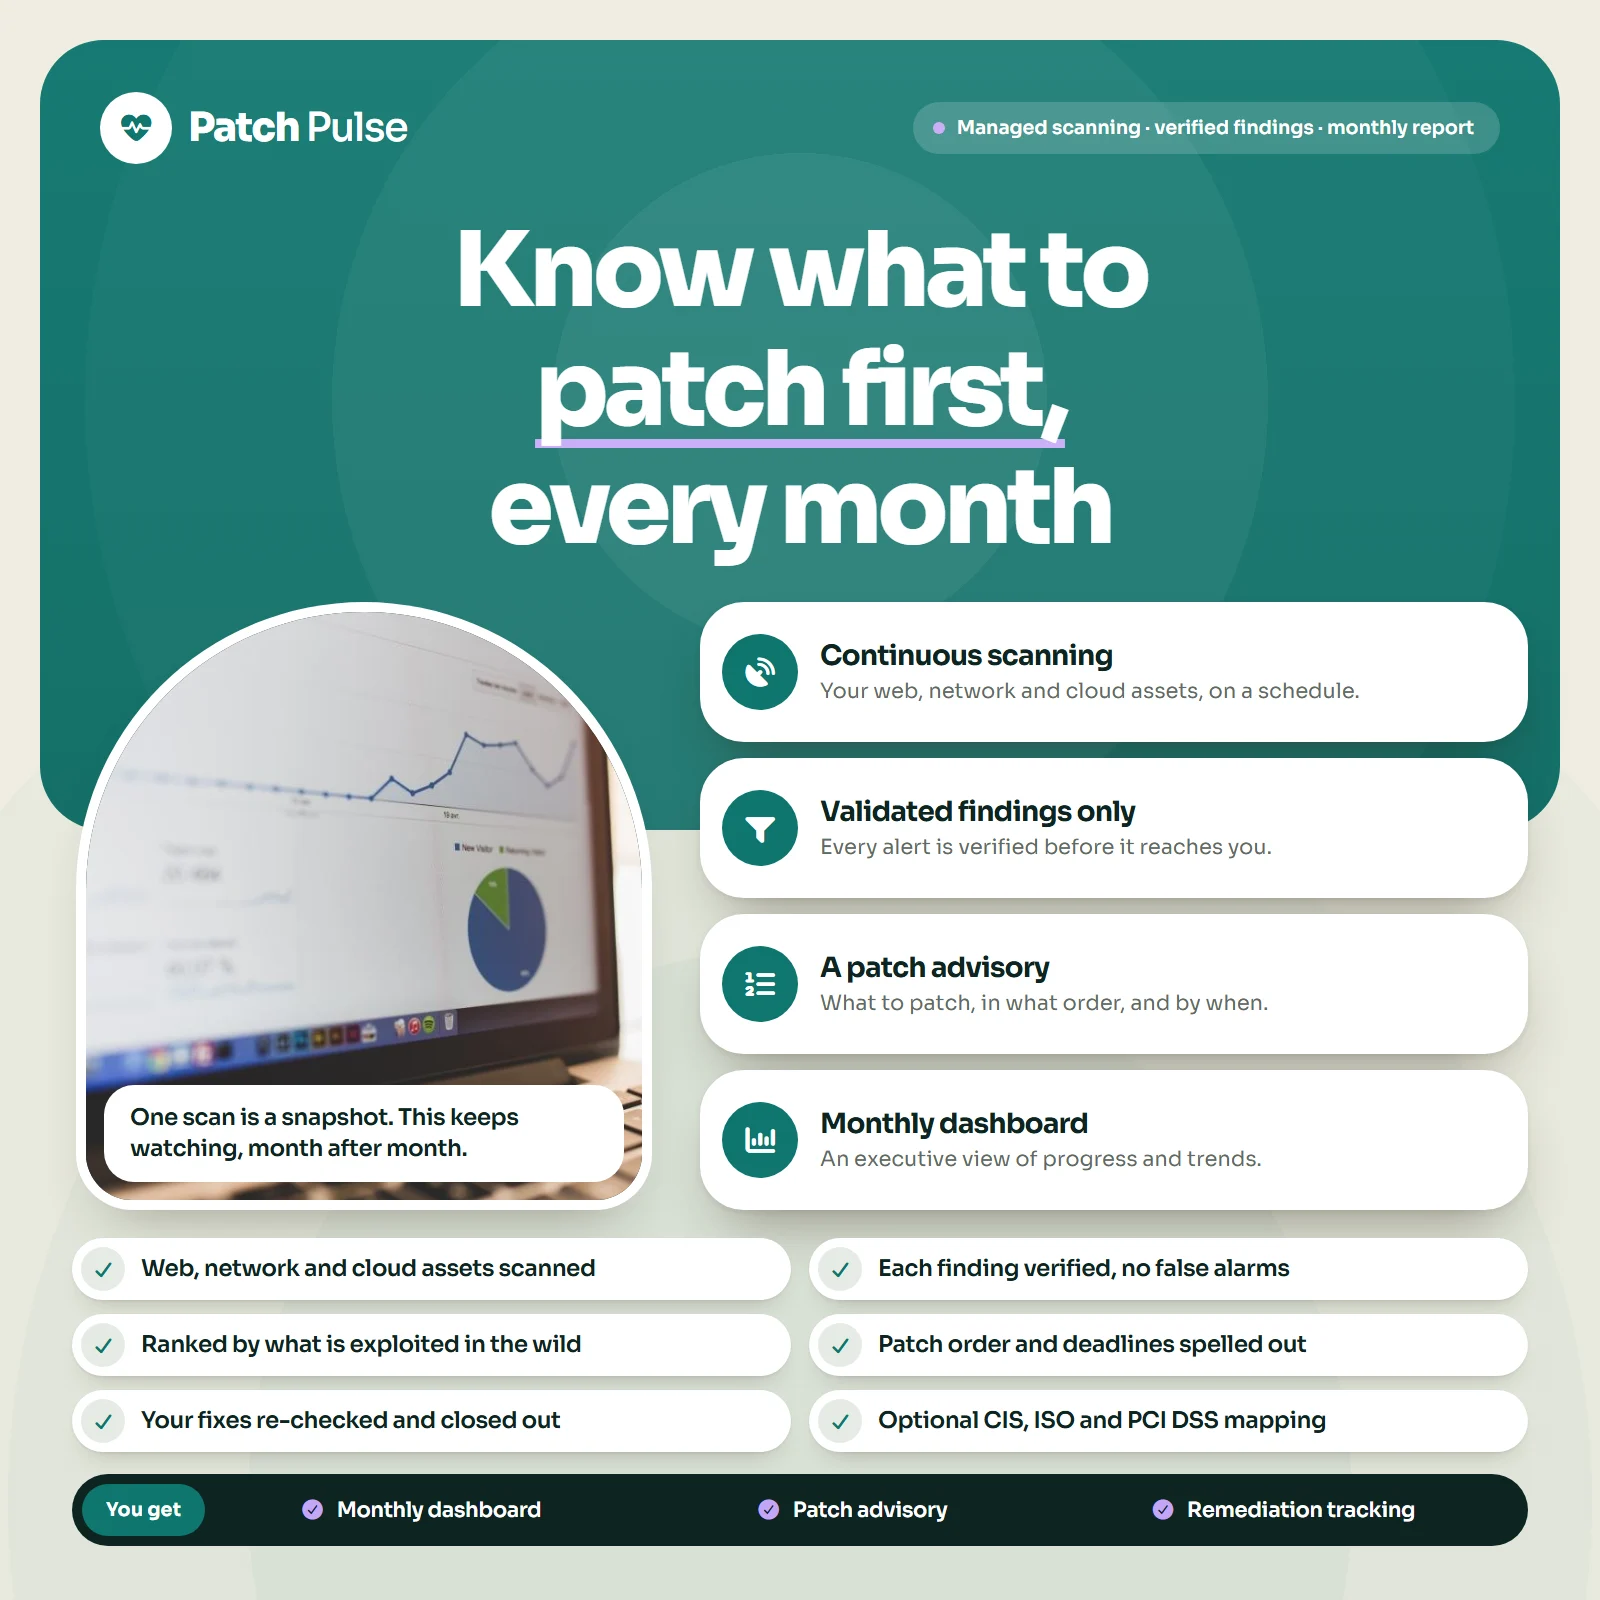
A one-off scan is a photo. Vulnerability Management is a heartbeat.
✅ Continuous scanning of web, network & cloud assets
✅ Only validated findings — every alert is verified, so no F/P noise
✅ Risk-based prioritization (what's exploitable in the wild, first)
✅ Patch advisory: what to patch, in what order, by when
✅ Remediation tracking — we check your fixes and close them out
✅ Monthly executive dashboard & trends
✅ Optional compliance mapping (CIS, ISO, PCI DSS)
What You Need to Share
📋 Asset inventory (or we help build it), scan-window preferences, and access for periodic authenticated scanning (Pro+).
Why It's Worth It
💰 The average org takes **60+ days** to patch critical vulns. Attackers weaponize them in hours. Continuous VM keeps your "days to patch" measured in days — and your auditors happy.
Timeline
⚙️ Onboarding: 3–5 days · Scans: monthly (Starter) / weekly (Pro) / continuous (Enterprise)
What’s included
- Continuous vulnerability scanning
- Validated findings only
- Risk-based prioritization
- Patch advisory & SLAs
- Remediation tracking
- Monthly dashboards
- Compliance mapping
No reviews yet. Be the first to review this product!